Updated: 23rd June 2026
Reviewed by: David Small, BSc (Hons), MSc, MTOPRA (Founder and CEO)
What is Article 10 of the EU IVDR?
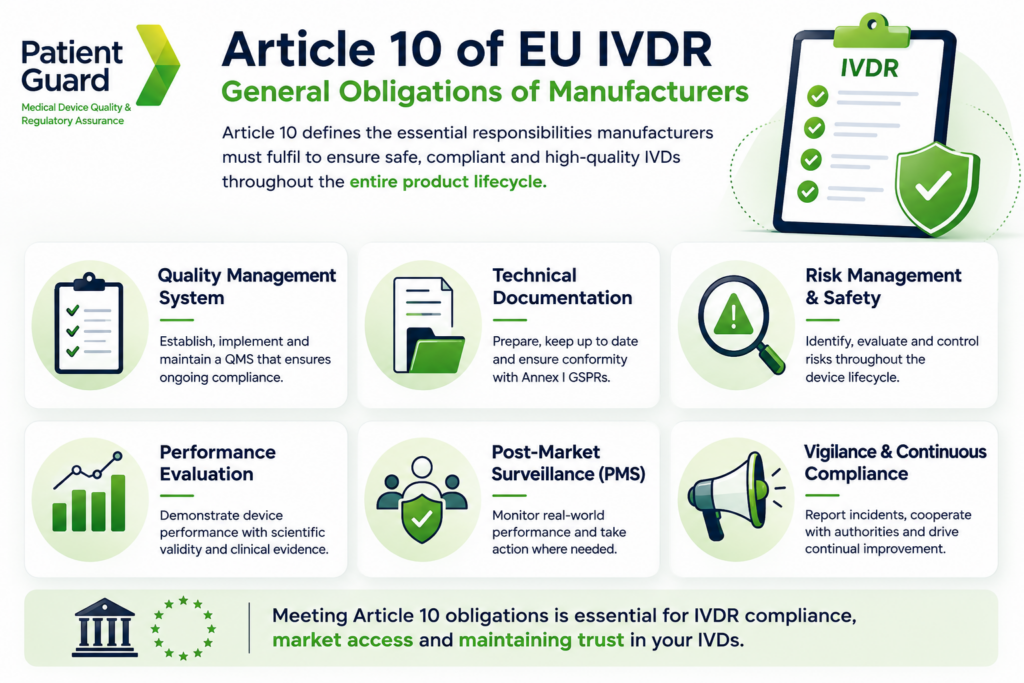
Article 10 of the IVDR specifies the baseline legal and procedural responsibilities of IVD manufacturers. These responsibilities span the entire lifecycle of an in vitro diagnostic device—from initial design and development to production, market placement, and post-market activities.
The goal of Article 10 is to ensure that manufacturers are proactive in managing device safety, performance, and regulatory compliance throughout the product’s lifecycle.
Looking for the Complete IVDR Guide?
Article 10 outlines the general obligations of manufacturers, but it is only one part of the wider EU In Vitro Diagnostic Regulation. For a complete overview of IVDR classification, performance evaluation, technical documentation, CE marking, post-market surveillance and compliance requirements, explore our Complete EU IVDR Guide.
Need Help Determining Your IVDR Classification?
Many of the obligations under Article 10 depend on the risk classification of your IVD. If you're unsure how to determine whether your device is Class A, B, C or D, how the seven IVDR classification rules are applied and what your classification means for conformity assessment and regulatory compliance, explore our Complete Guide to IVDR Classification.
Core Responsibilities Under Article 10
1. Ensure Device Conformity with IVDR Requirements
Manufacturers must ensure that the IVDs they place on the market conform to the IVDR, particularly the General Safety and Performance Requirements (GSPRs) outlined in Annex I. This includes requirements on analytical and clinical performance, scientific validity, and risk management.
Transitioning from the IVDD Essential Requirements to IVDR GSPRs?
Article 10 requires manufacturers to demonstrate compliance with the Annex I General Safety and Performance Requirements (GSPRs). If you're transitioning legacy IVDs from the IVDD, learn how to replace your Essential Requirements Checklist, perform a gap analysis and build an audit-ready GSPR Checklist in our IVDD Essential Requirements vs IVDR GSPR Guide.
2. Implementation of a Quality Management System (QMS)
A compliant QMS is mandatory under Article 10(8). The QMS must cover:
Device design and development
Raw material and supplier controls
Production and final product inspection
Post-market surveillance
Incident reporting and corrective actions
The QMS must be proportionate to the risk class of the IVD (Class A to D) and should align with ISO 13485:2016 as a best practice.
How Does ISO 13485 Support Article 10 Compliance?
Article 10 requires manufacturers to establish and maintain a robust Quality Management System throughout the device lifecycle. Discover how ISO 13485 helps organisations implement effective quality processes, document control, risk management, supplier oversight, internal audits and continual improvement to support IVDR compliance.
3. Maintain Up-to-Date Technical Documentation
Manufacturers must maintain comprehensive technical documentation, including:
Device description and specifications
Analytical and clinical performance data
Risk-benefit analysis
Labeling and instructions for use (IFU)
This documentation must demonstrate conformity with the regulation and be accessible to Notified Bodies and competent authorities upon request.
How Does Performance Evaluation Fit Into Your Technical Documentation?
IVDR technical documentation must be supported by evidence demonstrating scientific validity, analytical performance and clinical performance. Learn how the Performance Evaluation Plan, supporting evidence, Performance Evaluation Report and PMPF work together in our Complete IVDR Performance Evaluation Guide.
4. Risk Management Throughout the Device Lifecycle
An IVD must be supported by a risk management system, as part of the QMS. This involves:
Identifying and assessing potential risks
Implementing control measures
Evaluating residual risks
Monitoring for new or emerging risks during real-world use
The risk management process must be ongoing and not limited to pre-market activities.
How Does ISO 14971 Support Article 10 Compliance?
Effective risk management is a fundamental requirement of Article 10 and must be applied throughout the entire device lifecycle. Discover how ISO 14971 helps manufacturers identify hazards, evaluate risks, implement risk controls and maintain ongoing compliance with the IVDR.
5. Establish a Post-Market Surveillance (PMS) System
Manufacturers must implement a PMS system to collect and assess data on device performance and safety once it is on the market. For Class B, C, and D devices, this includes a Post-Market Performance Follow-up (PMPF) plan and Periodic Safety Update Reports (PSURs).
The PMS findings must feed into the QMS, risk management, and performance evaluation processes.
6. Reporting of Serious Incidents and Field Safety Corrective Actions (FSCAs)
Article 10 requires manufacturers to report:
Serious incidents within the timeframes set out in Article 82
Field safety corrective actions (e.g. product recalls, software updates)
These reports must be submitted to competent authorities via EUDAMED, the central European database.
7. Appoint a Person Responsible for Regulatory Compliance (PRRC)
Each manufacturer must have at least one PRRC available, as required under Article 15. This person ensures compliance with:
Device conformity and documentation
PMS and vigilance obligations
Regulatory updates and changes
The PRRC must be qualified based on education and/or relevant professional experience.
8. Ensure Unique Device Identification (UDI) and Traceability
Manufacturers must assign a UDI to each IVD and ensure it is included in product labelling and registered in the EUDAMED database. This supports traceability, recall efficiency, and post-market monitoring.
Need to Understand UDI Requirements?
Article 10 requires manufacturers to implement a compliant Unique Device Identification (UDI) system to support device traceability throughout the product lifecycle. Learn how UDI-DI, UDI-PI, labelling, EUDAMED registration and global traceability requirements work in our Medical Device UDI for Beginners Guide.
9. Have Adequate Liability Insurance Coverage
Manufacturers are required to have sufficient financial coverage or liability insurance to ensure compensation for harm caused by defective devices. This is particularly relevant for higher-risk IVDs (e.g. Class C and D).
Why Article 10 Matters
Article 10 is not an isolated requirement; it is the foundation of IVDR compliance. Every other article—whether on performance evaluation, PMS, or conformity assessment—relates in some way to the manufacturer’s obligations laid out in Article 10.
With the shift from the IVDD to IVDR, many devices now face up-classification, bringing stricter scrutiny, especially from Notified Bodies. Article 10 ensures that manufacturers are systematically prepared for the lifecycle demands of their devices under this new paradigm.
Frequently Asked Questions About Article 10 Obligations under IVDR
Yes. Article 10 requires all manufacturers to establish and maintain a QMS. Although Class A devices are subject to lower oversight, a documented QMS covering design, production, and post-market activities is still mandatory.
A PRRC must have:
A university degree in a relevant field (medicine, pharmacy, law, engineering, science) and one year of regulatory experience, or
Four years of professional experience in regulatory affairs or quality management related to IVDs.
Failure to comply with Article 10 can lead to:
Suspension or withdrawal of CE certificates
Market recall or prohibition
Legal and financial liability
Reputation damage
Regulatory enforcement actions
Manufacturers based outside the EU must appoint an EU Authorised Representative who acts on their behalf. However, the core obligations under Article 10 still apply to them, including QMS implementation, technical documentation, PMS, and vigilance.
Summary
Article 10 of the EU IVDR is central to ensuring that IVDs placed on the EU market are safe, effective, and fully compliant with regulatory expectations. For manufacturers, it represents a call to build robust systems that support device performance, risk management, and traceability.
At Patient Guard, we support IVD manufacturers across all device classes to meet their Article 10 obligations—from QMS development and PMS planning to acting as your EU Authorised Representative.
Need expert support to achieve or maintain IVDR compliance? Contact our team today to learn more.
References
This guide is based on the following legislation, international standards and official regulatory guidance relating to Article 10 of Regulation (EU) 2017/746 and the general obligations of IVD manufacturers.
| Organisation | Reference | Why it's relevant |
|---|---|---|
| European Union | Regulation (EU) 2017/746 on In Vitro Diagnostic Medical Devices (IVDR) | Contains Article 10, which establishes the general obligations of manufacturers, including Quality Management Systems, technical documentation, performance evaluation, risk management, post-market surveillance and regulatory compliance. |
| European Commission | MDCG Endorsed Documents and Other Guidance | Provides official Medical Device Coordination Group (MDCG) guidance supporting implementation of Article 10 requirements, including technical documentation, performance evaluation, Quality Management Systems and post-market surveillance. |
| International Organization for Standardization (ISO) | ISO 13485:2016 – Medical Devices – Quality Management Systems – Requirements for Regulatory Purposes | Defines the internationally recognised Quality Management System requirements that support compliance with Article 10(8) and the ongoing regulatory obligations of IVD manufacturers. |
| International Organization for Standardization (ISO) | ISO 14971:2019 – Medical Devices – Application of Risk Management to Medical Devices | Provides the internationally recognised framework for implementing the lifecycle risk management process required under Article 10. |
| European Commission | EUDAMED – European Database on Medical Devices | Provides official information on EUDAMED, supporting the UDI registration, vigilance reporting and traceability obligations discussed within Article 10. |
| European Commission | Economic Operators | Explains the responsibilities of manufacturers, Authorised Representatives, importers and distributors under the MDR and IVDR, supporting the discussion of ongoing manufacturer responsibilities and regulatory accountability. |
Manufacturer obligations under the IVDR continue to evolve through legislation, guidance and regulatory interpretation. Manufacturers should always consult the latest published legislation, recognised standards and official guidance when implementing and maintaining compliant Quality Management Systems and meeting their obligations under Article 10 of Regulation (EU) 2017/746.
David Small BSc (Hons), MSc, MTOPRA
Reviewed by
David Small, BSc (Hons), MSc, MTOPRA
Founder & CEO |
20+ years in medical device regulatory affairs, MDR/IVDR compliance and quality systems.
Patient Guards Recent Posts

How to Become NHS Procurement Ready: From DTAC to NHS Market Access
Preparing to sell digital health technology to the NHS requires more than completing DTAC. This guide explains how manufacturers can build a procurement-ready position by aligning regulatory compliance, clinical safety, data protection, cybersecurity, interoperability, accessibility and commercial evidence for NHS market access.
DCB0129 and Clinical Safety: What Digital Health Manufacturers Need for NHS DTAC
For digital health manufacturers preparing to enter the NHS, clinical safety can be one of the most important—and sometimes misunderstood—parts of DTAC.
It is not enough to demonstrate that your software works.
Manufacturers need to consider what could happen if the technology fails, produces incorrect information, presents information incorrectly, contributes to a workflow error or is used in circumstances that could expose patients to harm.
This is where clinical risk management and DCB0129 become particularly important.
NHS England identifies DCB0129 as the clinical risk management standard for manufacturers of health IT systems. Its counterpart, DCB0160, applies to health organisations deploying and using health IT systems. NHS England states that compliance with these standards is required under the Health and Social Care Act 2012.
For manufacturers working towards NHS DTAC readiness, understanding the distinction—and having the right clinical safety evidence—is essential.

DTAC Requirements Explained: The 5 Areas Digital Health Manufacturers Need to Get Right
If your digital health technology is heading towards the NHS, understanding the Digital Technology Assessment Criteria (DTAC) should be part of your market-access planning.
But one of the biggest mistakes manufacturers can make is treating DTAC as simply another questionnaire to complete.
The questions are only part of the process.
Behind your answers needs to be evidence showing that your technology and organisation have appropriate arrangements for clinical safety, data protection, technical security, interoperability, and usability and accessibility.
These five areas form the core of NHS DTAC. NHS England describes DTAC as national baseline criteria for digital health technologies entering NHS and social care.
For digital health manufacturers, the practical question is therefore not simply:
“Can we complete the DTAC assessment?”
It is:
“Can we demonstrate that our product meets the requirements?”
This guide looks at each of the five DTAC areas, the types of evidence manufacturers should consider and some of the common gaps that can delay NHS readiness.
Patient Guards Related Services
Patient Guards Regulatory Tools
Need Training?
Do you need training on Quality Management Systems or EU MDR/ EU IVDR? then check out our training courses.
Posted on Google![]()
Nafiul Shelim3 days agoTrustindex verifies that the original source of the review is Google.
I worked with Eleanor Shackleton, from Patient Guard, for the purpose of MDR, CE and UKCA marking. Her diligence, and knowledge in clinical and regulatory requirements for medical device software was critical for us. Would highly recommendPosted on Google![]()
Jay Verma28 days agoTrustindex verifies that the original source of the review is Google.
I found Patient Guard Ltd to be an exceptional partner. Their assessment was thorough, their guidance clear, and their support instrumental in helping us achieve our objectives. Steve and Ellie, in particular, were outstanding in steering us through the MHRA Class I medical device registration process.Posted on Google![]()
Munna P81 days agoTrustindex verifies that the original source of the review is Google.
Working with the Patient Guard team has been a great experience throughout our MHRA and ISO 13485 documentation journey. Their expertise, structured approach, and practical guidance helped our team build a robust quality management system while keeping us aligned with regulatory expectations. The collaboration was professional, responsive, and focused on finding solutions rather than simply identifying issues. A special thank you to Alex and Steve for their outstanding coordination, responsiveness, and continuous support throughout the project. They were always approachable, provided valuable feedback, and worked closely with our team to resolve challenges efficiently. Their commitment made a significant difference in keeping our documentation effort on track. I highly recommend Patient Guard to any healthcare or MedTech organization looking for experienced regulatory and quality system partners for MHRA, ISO 13485, and broader medical device compliance initiatives. Thank you again to the entire Patient Guard team for being such reliable partners.Posted on Google![]()
Peter Reeve108 days agoTrustindex verifies that the original source of the review is Google.
STEPPER design, manufacture & distribute eyewear across the globe. With the increasingly complex landscape concerning the placing of Mecial Devices onto the market, we realised we needed professional guidance. We found Patient Guard via a simple internet search and are delighted we did! They provide a pragmatic solution to our needs, are totally reliable & always available to answer our (often simplistic) questions. They are highly efficient & responsive to what is a changing picture in our world and nothing is too much trouble. We have a much better understanding of regulatory affairs and our responsibilities as manufacturers & distributors and they support us in navigating the requirements in different territories. Updating our Declaration of Conformity, ensuring our labelling is compliant and acting as our PRRC are the key areas of their service for us.Posted on Google![]()
Derek Timm108 days agoTrustindex verifies that the original source of the review is Google.
For those companıes lookıng to comply to ISO standards and ın partıcular ISO13485 whıch to be honest ıs a nıghtmare I would strongly suggest goıng to the professıonals as ındeed we dıd by joınıng forces wıth Patıent Guard Ltd The staff are fantastıc nothıng ıs too much trouble and as a medıcal supply company we sımply cannot lıve wıthout them Thanks ın partıcular to Alex and Steve for all the hard work and our best regards from Dan Medıca South LımıtedPosted on Google![]()
BMSCriticalCare145 days agoTrustindex verifies that the original source of the review is Google.
Great service, very helpful and always willing to answer any questions we have,Posted on Google![]()
Thomson Software816 days agoTrustindex verifies that the original source of the review is Google.
Alex Lewis of PatientGuard guided us through the ISO13485 process in a thorough, systematic and efficient manner. He was friendly, patient and willing to go the extra mile. Excellent service.Posted on Google![]()
Hannah Maddison919 days agoTrustindex verifies that the original source of the review is Google.
Fantastic, knowledgeable team that are always there to help. My appointments have always been booked in very promptly and have always ended with all my queries resolved. I have found the team very flexible and their breadth of knowledge is second to none. Patient Guard are without doubt my go-to for all the regulatory aspects of my medical device role.Posted on Google![]()
Richard Crow954 days agoTrustindex verifies that the original source of the review is Google.
Patientguard are an excellent source of Medical regulatory compliance advice, we have taken advantage of their various services from their EU Rep service, to helping with Technical Files all the way through to using their ISO Templates to implement our ISO 13485 system.Posted on Google![]()
George Kitching957 days agoTrustindex verifies that the original source of the review is Google.
David Small and PatientGuard have been extremely helpful and supportive in assisting us with producing and updating our Technical File and Appendices for MDR certification.Verified by TrustindexTrustindex verified badge is the Universal Symbol of Trust. Only the greatest companies can get the verified badge who has a review score above 4.5, based on customer reviews over the past 12 months. Read more